How to Apply for Claude Mythos 5.2: Verification Guide
17 min read
Claude Mythos 5.2 (claude-mythos-5-2) is closed to general access; to unlock it, you must apply through Anthropic's Verification Portal under either the Cyber Verification Program (CVP) or the Life Sciences Verification Program (LSVP), provide tier-specific identity (KYC) or organizational evidence, attest to strict security controls, and then manually enable access in your API workspaces, Enterprise custom roles, or linked cloud accounts after approval. Mythos 5.2 shares the exact same underlying model weights, 1M-token context window, 128K max output, and $8 input / $40 output per MTok API pricing as Claude Fable 5.2, released November 9, 2026. The sole difference is that Fable 5.2's real-time cybersecurity and research-biology blocks are lifted or relaxed based on your verified tier.
This post is a guide compiled from Anthropic's official documentation, Help Center verification articles, and program announcements; as the author, I have not personally submitted a Claude Mythos 5.2 verification application. All UI paths, tier limits, deadlines, and document checklists were checked against Anthropic's primary pages as of November 19, 2026, and program terms can change over time. Sources are listed at the end. For Fable 5.2 pricing see the pricing and cost guide, and for standard subscription/API routes see how to access Claude Fable 5.2.
How verification works at a glance
Instead of blocking legitimate security and biology work with broad real-time refusals, Anthropic gates Mythos 5.2 behind upfront vetting, mandatory technical controls (such as phishing-resistant MFA and short-lived or disabled API keys), and 30-day post-approval abuse monitoring. Most applications run through the Verification Portal, yet approval alone does not turn the model on across most products: admins on Claude Console, Claude Enterprise, and cloud providers still have to wire up workspaces, custom roles, or account toggles before claude-mythos-5-2 stops throwing access blocks.
Before you apply: Do you actually need Mythos 5.2 verification?
Many teams apply for CVP assuming every security workflow requires Mythos 5.2. According to Anthropic's Help Center and product announcements, three common workflows work without going through verification at all:
- Everyday secure development: Reviewing your own code, patching known CVEs, triaging security alerts, and writing detection rules do not require CVP; Anthropic recommends using generally available models like Claude Fable 5.2 or Claude Opus 5.5.
- Claude Security on Enterprise: Claude Enterprise customers can run Claude Security to scan codebases for vulnerabilities without enrolling in CVP; Anthropic notes that Claude Security already runs on the full model family, including Claude Mythos 5.2, under the hood.
- When you genuinely need Mythos 5.2: On Fable 5.2, high-risk cyber requests (penetration testing, exploit generation, binary vulnerability work) fall back to Claude Opus 4.8, and most research-biology prompts fall back to Claude Opus 5. If your authorized defensive reverse engineering, exploit validation, red teaming, or dual-use biology R&D keeps hitting those classifiers, verification is required.
Program 1: Cyber Verification Program (CVP) and its three access tiers
On October 6, 2026 (with plan availability updated November 18, 2026), Anthropic merged Project Glasswing and its earlier CVP track into a single three-tier program. Every tier covers claude-mythos-5-2, claude-mythos-5-1, claude-opus-5-5, and claude-sonnet-5-5.
| Requirement / Detail | Defense Access | Red Team Access | Specialized Access |
|---|---|---|---|
| Permitted work | SOC, incident response, malware analysis, detection engineering, vulnerability triage and validation | Defense scope plus authorized pen testing, red teaming, adversary emulation, offensive tools and exploit dev | Authorized pen testing and red teaming of systemically important infrastructure (flight systems, power grids, telecom, interbank networks) and highest-severity techniques |
| Who can apply | Organizations and individuals | Organizations only | Organizations only |
| Eligible plans | Pro, Max, Ultra, Team, Enterprise, API and clouds (no Free plan) | Team, Enterprise, API and clouds | Team, Enterprise, API and clouds |
| Approved user limit | No default limit (individual covers you only) | Up to 75 approved users | Up to 25 approved users |
| Target review time | 2 days | 2 weeks (currently longer due to demand; Defense unlocks while waiting) | No set target; reviewed in depth with the US government |
| Mandatory security controls | MFA and API keys replaced at least every 7 days (tightens Dec 15, 2026) | Phishing-resistant MFA, company-domain accounts, org-controlled devices, outbound network controls, background checks, API key restrictions | All Red Team controls plus Single Sign-On (SSO) and managed devices with malware protection |
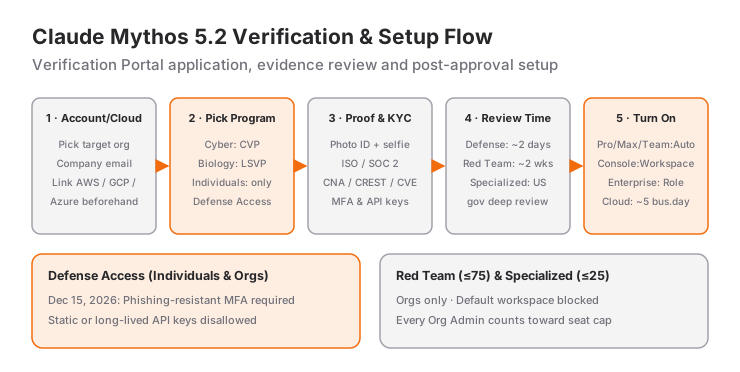
Critical December 15, 2026 Deadline (Defense Access): Starting December 15, 2026, Defense Access also requires phishing-resistant MFA (such as FIDO2 hardware keys or passkeys) and disallows static or long-lived API keys. Anthropic recommends migrating Console integrations to Workload Identity Federation ahead of that cutoff.
Anthropic also published CyScenarioBench benchmark results demonstrating how the tiers enforce boundaries (50 multi-stage trials running Claude Opus 5.5): without CVP, 0 of 50 tasks succeeded (blocked on the first prompt); under Defense Access, 46 of 50 trials were blocked and 4 completed; and under Red Team Access, zero blocks occurred and 34 of 50 tasks passed, matching the unguarded model's 67.6% baseline.
Absolute bans across all CVP tiers: Mass destruction of data or devices, denial-of-service (DoS) attacks, physical-world damage, extortion/ransomware, election interference, and any request with stated malicious intent remain strictly prohibited under Anthropic's Usage Policy.
What documents and evidence are actually required?
The fastest way to avoid a stalled or rejected application is providing independently verifiable proof. Anthropic explicitly cautions that screenshots and LinkedIn profiles usually are not enough. Upload full, dated PDFs or point reviewers to public registries, certificate directories, or issuer pages whose legal entity or personal name exactly matches the account being verified.
1. Individual applicants (Defense Access only)
Independent security researchers, open-source maintainers, and bug bounty hunters can apply only for Defense Access:
- Government photo ID (KYC): A physical, valid government-issued photo ID such as a passport, driver's license, state/provincial ID, or national identity card (photocopies and scans of copies are rejected), plus a phone with a camera for a live selfie check.
- Proof of defensive security work: A bug bounty platform profile (make sure privacy settings allow public viewing), open-source security maintainership records, CVE credits, published research, or defensive certifications.
2. In-house red teams (Corporate security)
Internal corporate red teams applying for Red Team Access must prepare four items:
- Organization details: Legal entity name, registered address, business registration number, and a company-domain email address.
- Proof of an established security program (at least one): The cybersecurity section of your latest annual report, a current ISO/IEC 27001 certificate, a SOC 2 Type II report, or a paid bug bounty program active for at least 12 months (critical infrastructure operators may also use a sector security obligation and must provide their sector registry listing).
- Team & advance authorization proof: Testing team name, lead's name, approximate headcount, and confirmation that every test is authorized in advance by someone with authority over the target systems.
- Offensive capability proof (at least one): Team members holding offensive security certifications (
OSCP,GPEN,CREST Registered Tester), public conference talks/research, or a redacted internal test report.
3. Cybersecurity and penetration testing firms
Security consultancies applying for Red Team Access qualify along the primary track if they hold any one of these credentials in the firm's own legal name:
- CVE Numbering Authority (CNA) listing
- Full membership in FIRST (Forum of Incident Response and Security Teams)
- A recent CVE credit
- A recognized testing accreditation such as CREST, CHECK, or FedRAMP 3PAO
Smaller or boutique pen-test firms without those four proofs must provide all four items from the alternative checklist: business registration at least one year old, a public website page describing testing services, at least two testers holding offensive certifications (OSCP, GPEN, CREST), and a redacted Statement of Work (SOW), redacted test report, or client reference from the past 12 months.
4. Government red teams & Specialized Access applicants
Government red teams provide their team name, lead, headcount, advance authorization confirmation, and offensive certs/public work/redacted internal report. Organizations seeking Specialized Access face deep joint review with the US government: operating critical infrastructure does not qualify on its own; you must prove formal authorization to test systemically important systems and explain specifically what work remains blocked under Red Team Access.
Step-by-step CVP application walkthrough
To avoid locking your application to the wrong organization or failing cloud verification, follow these four steps in exact order:
Step 1: Pick the right account, organization, and email first
In Anthropic's account system, your Claude web/app organization and your Claude Console (API) organization are completely separate, and CVP approval does not transfer between organizations. Apply from the exact organization where you intend to invoke claude-mythos-5-2. If applying as a company, create/use an account with your company email domain (email addresses cannot be changed later). Submit only one application per organization, submitted by an Owner / Primary Owner (Claude plans) or Admin (Claude Console).
Step 2: Link cloud accounts before submitting (AWS, Google Cloud, Azure)
If you plan to call claude-mythos-5-2 via Claude Platform on AWS, Claude Platform on Google Cloud, Google Cloud Agent Platform, Amazon Bedrock (global.anthropic.claude-mythos-5-2), or Microsoft Foundry, link your cloud accounts before submitting your application. You can create a free Anthropic account with no billing attached, though you cannot apply until you link a cloud account or add Console credits (you can link up to 10 AWS accounts or 10 GCP projects):
- In the Verification Portal, go to Linked accounts > Link account and choose your provider.
- AWS (Claude Platform on AWS and Bedrock): Enter your 12-digit AWS account ID and create the verification IAM role via the portal's launch link or CLI command. (Link Claude Platform on AWS before linking Bedrock. Note that Bedrock CVP currently requires a data retention exemption until Enterprise Frontier Safeguards becomes available there.)
- Google Cloud: Enter your Project ID (not the numeric project number) and execute the displayed
gcloudcommand to prove admin ownership. - Microsoft Foundry (Azure): Deploy a Claude model inside Foundry first, then enter your Subscription ID and Directory (Tenant) ID and run the Azure CLI commands displayed in the portal.
- Click "I've granted access", then "Verify".
Step 3: Complete the portal form, KYC/KYB, and control attestations
Sign in to the Verification Portal, open Programs, select Cyber Verification Program, and click Apply. Choose Business (organizations; Team, Enterprise, or API required for Red Team/Specialized) or Individual (Defense Access only). Select your tier, attach verifiable evidence links or full dated PDFs, attest to every required security control, accept the terms, and submit.
Two strict rules to know before clicking submit: applications cannot be edited or canceled once submitted (you can download a PDF copy of your submitted form and terms from the portal afterwards), and if rejected, you must wait seven days before reapplying with stronger evidence.
Step 4: Serving clients? Apply separately for External Use
Standard CVP approval covers Internal Use only (your own organization's systems, products, or independent bug bounty research/coordinated disclosure). If you test client systems or ship a security offering, once your organization receives internal CVP approval you must open Cyber productization > Register an offering in the Verification Portal.
Currently, Anthropic is accepting applications for Managed service (~1 week review): your staff prompt Claude while clients receive only human-reviewed deliverables and never see raw model output. You will need a designated security contact, the name and title of a signing corporate officer, and acceptance of the Anthropic Cyber Defender Partner Addendum. Constrained and Unconstrained customer-facing products are currently open for expression of interest only. Routing client traffic through CVP without explicit External Use approval violates terms and is grounds for removal.
Crucial post-approval step: Turning on Mythos 5.2
One of the most frequent issues reported in Anthropic's FAQ is: "I'm approved, why am I still blocked?" On Console, Enterprise, and cloud providers, approval only grants eligibility — an admin must manually enable the tier:
- Claude Pro, Max, Ultra, and Team: Enables automatically upon approval. On Team plans, access applies to every seat, so Red Team (>75 seats) or Specialized (>25 seats) stays disabled if your team exceeds the tier cap. Billing note: on Pro, Mythos models work only with usage credits; on Max and Ultra, Mythos and Fable share up to 50% of your weekly usage limit before falling back to credits.
- Claude Console (First-Party API): Does not turn on automatically. An Organization Admin must:
- Create a new workspace or choose an existing one (you cannot assign CVP to the
Defaultworkspace). - Add only authorized users to that workspace.
- Open Console > Programs, click your approved tier card, and toggle Access ON in the Workspaces table.
- Resolve any cell showing
"Not set","Not met", or"Allowed"until your active workspace count confirms activation (for example,"1 of 2 workspaces active"). Red Team and Specialized require API keys turned off on the workspace; Defense Access allows API keys expiring within 7 days until December 15, 2026, after which API keys are disallowed there as well. - Watch the seat counter trap: For Red Team (75) and Specialized (25), every Organization Admin counts as a seat alongside workspace members. Exceeding the limit disables CVP across all workspaces until you are back within cap.
- Create a new workspace or choose an existing one (you cannot assign CVP to the
- Claude Enterprise: Built-in roles are not covered. As Owner or Primary Owner, open Organization settings > Roles, create or edit a Custom role, select eligible groups under the Details tab, and enable your CVP/LSVP grant under Models > Grants.
- AWS, Google Cloud, and Microsoft Foundry: In the Verification Portal, open the Cyber Verification Program page and flip your tier ON under Access on linked accounts. On Google Cloud Agent Platform, you must also accept the Advanced AI Safety Addendum on the Claude model in Model Garden and run Google's
setPublisherModelConfigAPI to setdataSharingEnabledProvidertoANTHROPICfor each model and region. Provisioningclaude-mythos-5-2on cloud providers takes about five business days after CVP approval (committed-contract customers also complete a short account-team form and accept a private marketplace offer).
Program 2: Life Sciences Verification Program (LSVP) for biology & R&D
The second official route to claude-mythos-5-2 is the Life Sciences Verification Program (LSVP), launched in beta on September 17, 2026 for biotech startups, pharmaceutical companies, and academic labs. LSVP unlocks permissive biology safeguards on Mythos, Opus, and Sonnet across drug discovery, clinical development, biomanufacturing, and basic research.
- Who qualifies right now: Currently open to organizations and teams on Claude Enterprise, Claude Team, Claude Platform (API), and Claude Science. Free, Pro, Max, and Ultra individual plans are not eligible yet, and LSVP is unavailable on third-party clouds or BAA/HIPAA-enabled organizations handling Protected Health Information (organizations with PHI must use a separate non-BAA org for LSVP work).
- Two grant levels:
- Standard Use: Covers most day-to-day R&D, quality assurance, regulatory, and manufacturing biology workflows across an entire team; renewed annually.
- High-risk Use: A project-specific add-on that removes all life sciences blocks for one declared dual-use project (such as characterizing viral vector immune interactions); renewed every 6 months. High-risk Use grants for Claude Mythos are reviewed in collaboration with the US government for a narrow set of qualified entities.
- How to apply & how monitoring shifts: Admins register organizational interest through Anthropic's LSVP form (
claude.com/form/life-sciences-verification-program), after which Anthropic vets institutional research credibility, biosecurity controls, and ethical oversight. Rather than real-time blocks, LSVP switches to 30-day offline pattern monitoring against the organization's declared safe scope (no IP or sensitive experiment details are put in grant descriptions). LSVP does not lift cybersecurity safeguards.
30-day data retention vs. Enterprise Frontier Safeguards (EFS)
Both CVP and LSVP require 30-day prompt and response retention by default so Anthropic can detect multi-session misuse, credential theft, or autonomous misbehavior. Anthropic states retained data is strictly compartmentalized and never used to train models.
If your organization operates under banking, healthcare, legal, or public-sector rules that prohibit leaving prompts on Anthropic's servers, you have two compliant paths:
- Existing ZDR exemption: Organizations already holding an official Anthropic zero data retention (ZDR) exemption for Fable or Mythos can run internal CVP workloads with ZDR.
- Enterprise Frontier Safeguards (EFS): Rolling out to eligible enterprises (
claude.com/form/enterprise-frontier-safeguards), EFS stores retained monitoring logs directly inside your own Amazon S3, Azure Blob Storage, or Google Cloud Storage bucket under Customer-Managed Encryption Keys (CMEK), and routes automated safety alerts directly to your own internal security team without Anthropic human review.
Frequently Asked Questions
Can an individual developer or researcher apply for Claude Mythos 5.2?
Yes, but only under CVP Defense Access and with a paid Pro, Max, Ultra, Team, Enterprise, or Console API plan (not the Free plan). Individual verification requires a physical government-issued photo ID plus a live smartphone selfie, alongside publicly verifiable defensive cyber proof such as an active bug bounty profile, CVE credits, or open-source security maintainership. Individual accounts cannot apply for Red Team Access, Specialized Access, or LSVP.
Why is claude-mythos-5-2 still blocked after my CVP application was approved?
Approval does not automatically activate CVP on Claude Console, Claude Enterprise, or cloud platforms. On Console, you must create or pick a non-Default workspace, toggle Access ON under Console > Programs, resolve API key restrictions (off for Red Team/Specialized, and off everywhere in Defense Access after Dec 15, 2026), and keep total workspace users plus all Org Admins within the 75- or 25-seat cap. On Enterprise, assign a Custom role with the grant attached. Cloud provisioning takes around five business days after approval.
What happens if my verification application is denied?
You retain normal access to generally available models such as Claude Fable 5.2, Opus 5.5, and Sonnet 5.5, plus any lower CVP tier you did qualify for. You can reapply after seven days once you can supply stronger, independently verifiable documentation (full dated PDFs or public registries rather than screenshots or LinkedIn links) and verify you applied from the right account type and target organization.
Can a pen-testing firm use its CVP tier on client engagements right away?
No. Default CVP approval authorizes Internal Use only (your own systems or independent bug bounty research). To perform client work or ship a service, an Owner or Console Admin must submit a separate External Use offering under Cyber productization > Register an offering in the Verification Portal, starting with Managed service (~1 week review) and signing the Anthropic Cyber Defender Partner Addendum.
Do I need CVP just to audit my company's codebase for bugs?
Not necessarily. Standard code review, patching known bugs, finding vulnerabilities in source code you own, and triaging everyday alerts work on Fable 5.2 and Opus 5.5 without CVP. Additionally, Claude Enterprise teams can run Claude Security (which runs on Mythos 5.2) without applying to CVP at all.
Sources
- Anthropic Help Center, Cyber Verification Program: three access tiers, evidence requirements by org type, KYC/KYB, cloud account linking, Console/Enterprise/Vertex AI setup, Dec 15, 2026 MFA/API key deadline, External Use rules.
- Anthropic Platform Docs, Claude Mythos 5.2 Overview: model IDs (
claude-mythos-5-2,global.anthropic.claude-mythos-5-2), 1M context, $8 / $40 pricing, verification status and lifecycle. - Anthropic News, Expanding the Cyber Verification Program (October 6, 2026; updated November 18, 2026): Glasswing consolidation, CyScenarioBench tier evaluation, updated Team/Enterprise/API eligibility.
- Anthropic News, Introducing the Life Sciences Verification Program (September 17, 2026; interest form: Life Sciences Verification Program): Standard Use vs. High-risk Use grants, 30-day offline monitoring, BAA/PHI restrictions.
- Anthropic News, Developing Enterprise Frontier Safeguards with our customers (September 1, 2026; interest form: Enterprise Frontier Safeguards): customer-managed cloud storage (S3, Azure Blob, GCS), CMEK, and customer-routed monitoring alerts.
- Anthropic News, Introducing Claude Fable 5.2 and Claude Mythos 5.2 (November 9, 2026): shared model architecture, Claude Security, fast mode availability.
Related Posts
What Is Claude Fable 5.2? Price, Mythos, Access
Anthropic released Claude Fable 5.2 on Nov 9, 2026: 1M context, $8 input and $40 output per million tokens, 20% cheaper than Fable 5.1.
What Can Claude Fable 5.2 Do? 1,000 Agents, Fermat
According to Anthropic, Claude Fable 5.2 built an OS with 1,000 agents, formalized Fermat's Last Theorem in 30 hours, and solved two open physics problems.
Migrating Claude Fable 5.1 to 5.2: API Changes
Swapping claude-fable-5-1 for claude-fable-5-2 is not enough: the prefix check, thinking blocks, computer_toolset_20260801 and advisor pairing are breaking.